How to Choose a Cyber Security Framework for a Small Business
The right framework gives your business a common language for risk, clear priorities and evidence that security controls are actually working.
Reviewed by Connected Platforms | Updated September 2026
What a cyber security framework does
A framework turns “be secure” into a structured set of outcomes, controls and evidence. It helps leadership and technical teams agree on priorities, track progress and explain the organisation’s position to customers, insurers and partners.
A framework does not replace risk assessment or good IT management. It gives those activities a repeatable structure.
Compare the main options
Essential Eight
Best when an Australian organisation needs a focused technical baseline against common threats.
SMB1001
Best when a small or medium business wants a staged standard and a potential certification pathway.
ISO 27001
Best when contracts, customers or governance require a formal information security management system.
NIST Cybersecurity Framework
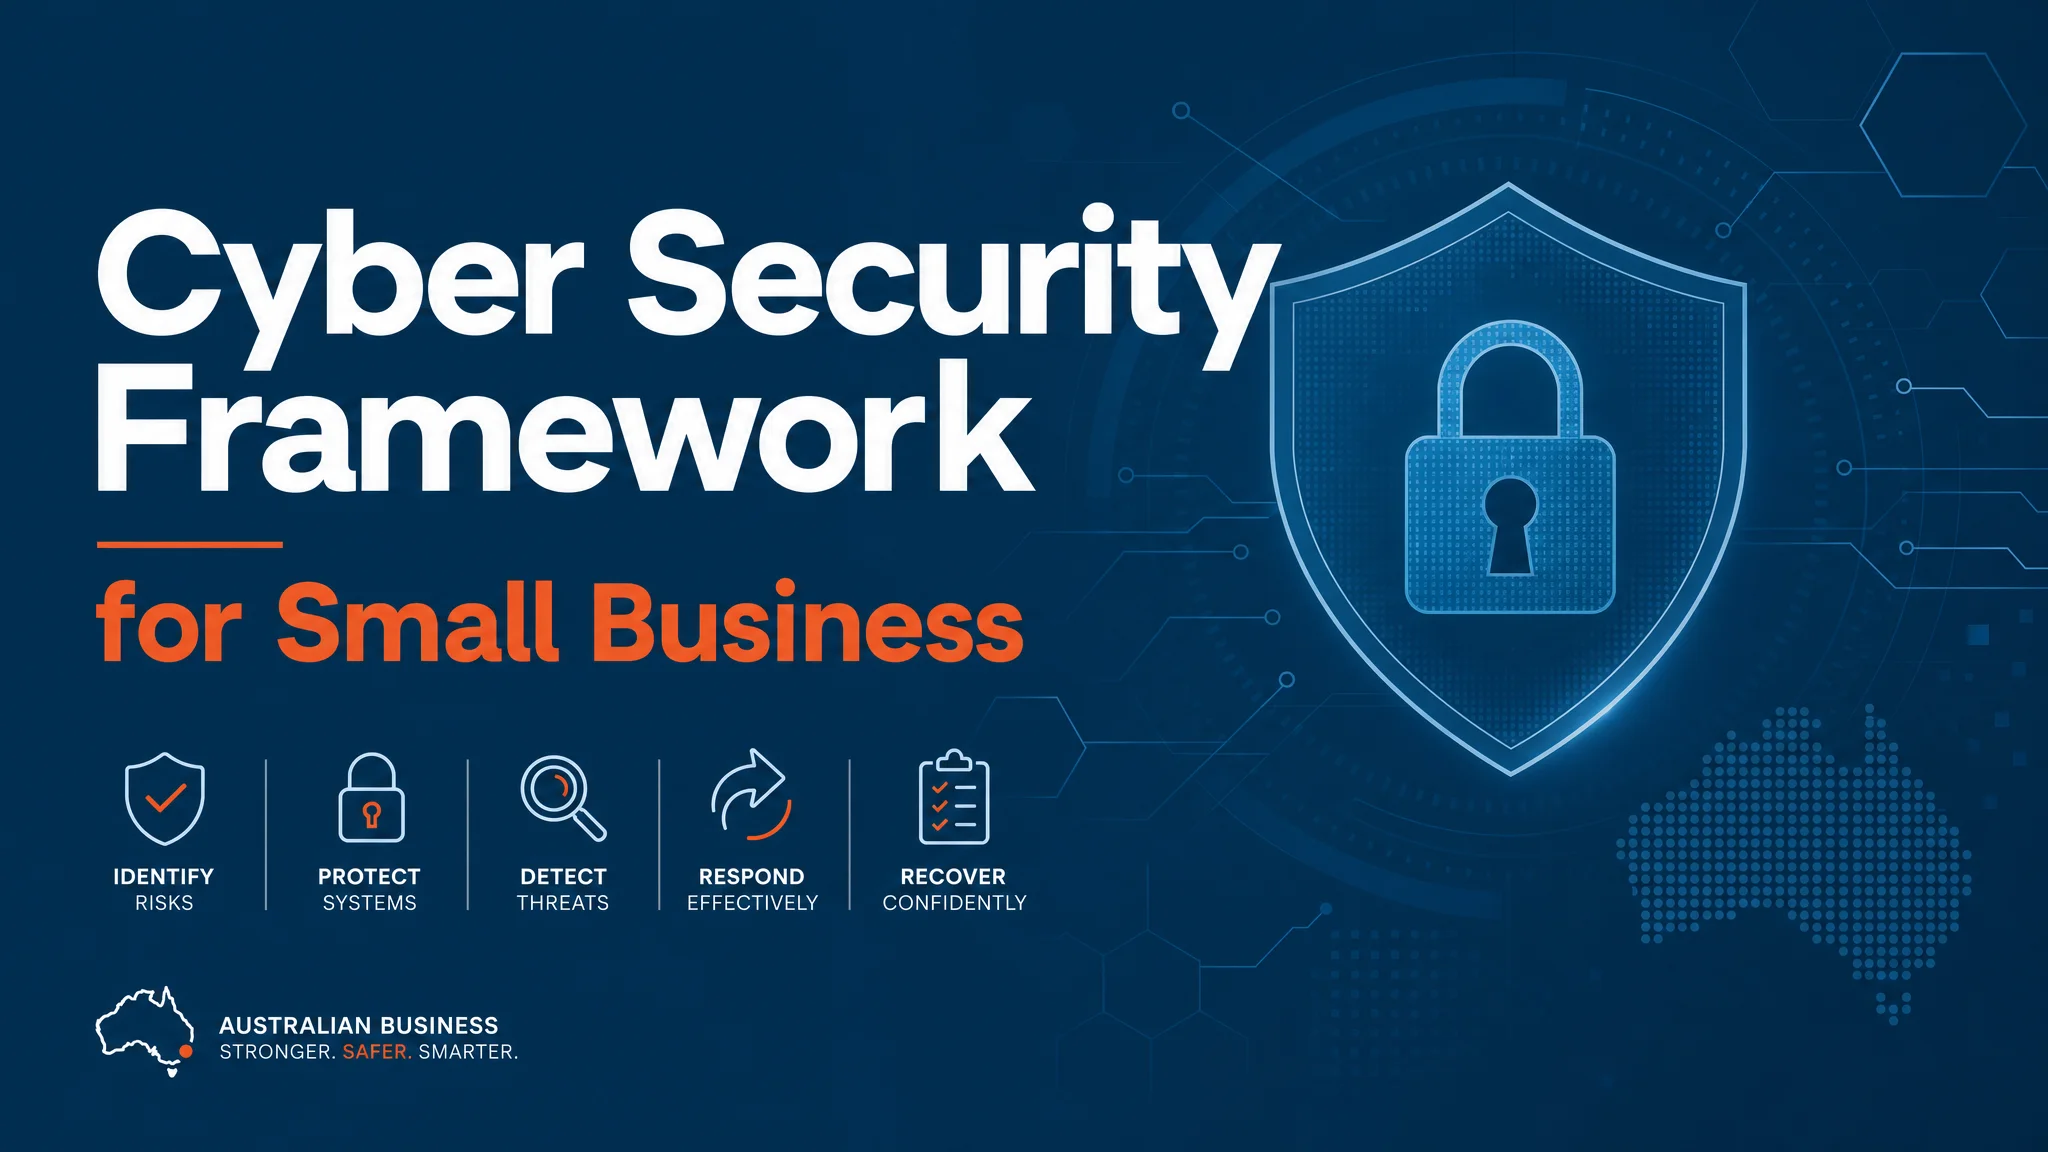
Best when an organisation needs a flexible risk framework spanning governance, identify, protect, detect, respond and recover.
How to choose without overcomplicating it
Start with the requirement
Identify whether the driver is risk reduction, a customer request, cyber insurance, a tender or formal certification.
Define what is in scope
List the systems, data, locations, people and suppliers the framework needs to cover.
Assess current controls
Check what is implemented, who owns it and what evidence exists.
Choose a realistic target
Select the framework and maturity target that match the business requirement.
Create an improvement plan
Prioritise the controls that reduce the most material risk and assign owners and review dates.
Evidence matters more than assumptions
A policy, licence or security product does not prove a control is working. Useful evidence can include configuration records, access reviews, patch reports, backup restoration tests, incident exercises and approved exceptions.
- Test controls instead of relying only on screenshots or checklists.
- Track exceptions with an owner, business reason and expiry date.
- Review the framework after material technology or business changes.
- Keep leadership reporting focused on risk, progress and unresolved decisions.
Cyber insurance is one input, not the framework owner
Insurers may ask about controls such as MFA, patching, backups and incident response. Requirements differ by insurer and policy. Confirm the exact questions and conditions rather than assuming one maturity level guarantees cover or a successful claim.
A good framework decision should still make sense if the insurance questionnaire changes next year.
Not sure which framework fits?
We can help you choose a sensible starting point, assess current controls and avoid unnecessary compliance work.